An experienced hand in the leadership team
Interim IT leadership that takes charge when it counts.
Interim assignments as IT manager or CIO, and consulting assignments in infrastructure and security, backed by real operational responsibility.
- 01 / Company
- Swedish limited company since 2019
- 02 / Experience
- 25+ years in IT leadership
- 03 / Product
- We build nisenta.com
Interim IT management, NIS2 advisory and software development.
We take on IT responsibility in the management team when the role is vacant, and have the expertise to secure and build what is needed as well.
Interim
Interim IT manager, CIO & IT leadership
We step in as acting IT manager or as IT expertise on the leadership team when the role sits empty, keeping momentum in infrastructure, security and digitalization until a permanent solution is in place. Management gets a solid basis for decisions, security is maintained and projects keep their pace.
Read more about interim IT managementMore on assignments in Hudiksvall and Stockholm
25+
Years in IT leadership and management teams
- 02
Nisenta
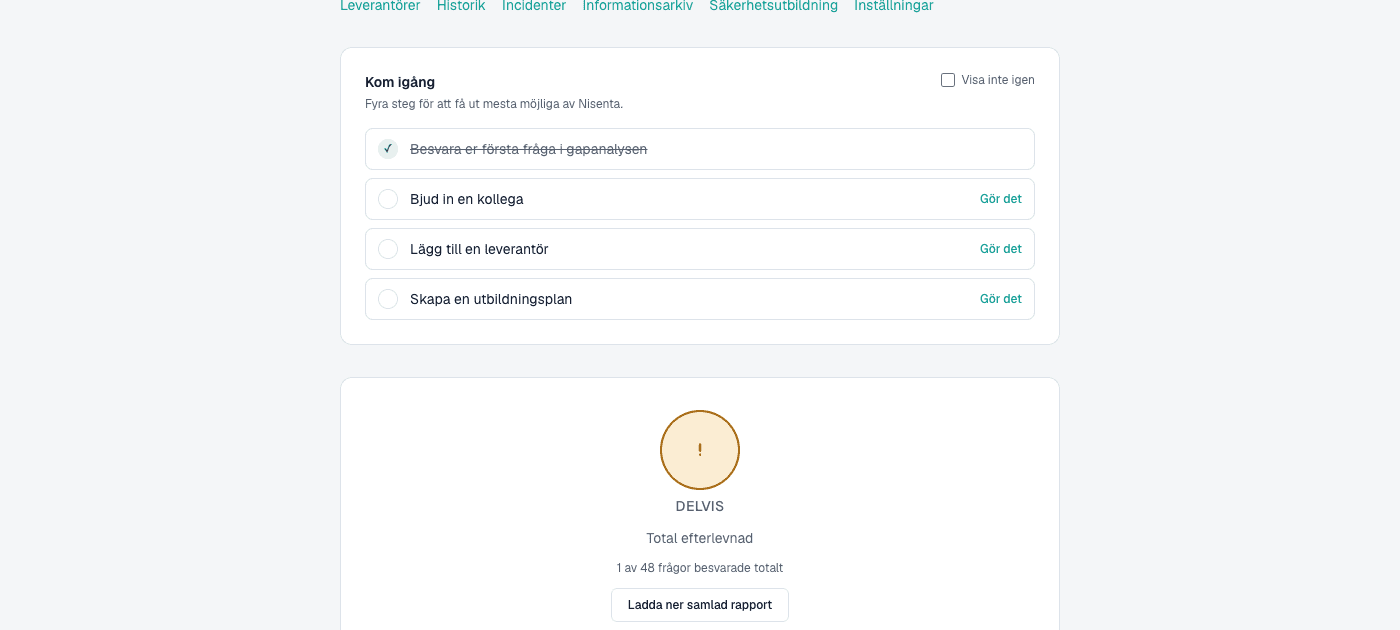
Our SaaS platform for ongoing compliance with NIS2, GDPR and the Cyber Resilience Act. Gap analysis, action plan, supplier follow-up and attestations in one place, for a fixed monthly cost.
Read about Nisenta - 03
NIS2, GDPR & CRA consultant
Concrete help interpreting and implementing the requirements of NIS2, GDPR and the Cyber Resilience Act: from gap analysis to an action plan you can actually follow. Whether or not you use Nisenta.
- 04
AI-driven development
We build internal tools, automate manual workflows and create AI assistants connected to your own data and documentation, faster from idea to production and without cutting corners on architecture, security or review.
- 05
IT security & security architecture
Networking, access control, encryption and incident readiness, grounded in real experience running systems that are not allowed to go down.
Straight to the point, no detours.
The same approach whether it's an interim assignment or a defined project.
Assessment
We review the current state (technology, risks and goals) and land on what actually needs to be done.
Plan
A prioritized plan with clear ownership, a timeline and what each step costs.
Delivery
We build, roll out and run the change, close to your own organization.
Follow-up
We measure the outcome, document it and hand over so you can maintain it yourselves.
Our product
Nisenta
Ongoing NIS2, GDPR and CRA compliance without consultant fees. Gap analysis, action plan, supplier follow-up and attestations, all in one place, for a fixed monthly cost.
Interim IT leadership built on real operational responsibility.
Comitt (CO Mitt AB) steps in as interim IT manager and CIO on leadership teams, with breadth from governance and regulatory compliance to security architecture, networking and our own software development.
The work is grounded in real experience running systems in production, not just theory. We take on few engagements at a time so we can go deep on each one.
61.73° N · 17.10° E
- On site
- Gävleborg · Stockholm
- Remote
- Rest of Sweden
Frequently asked questions
NIS2, GDPR & CRA compliance
Who is in scope for NIS2 in Sweden?
NIS2 applies to medium and larger organizations (roughly 50 employees or more, or over EUR 10 million in turnover) in sectors such as energy, transport, health, drinking and waste water, digital infrastructure, public administration, post, waste, chemicals, food, manufacturing and digital services. Some smaller entities are still covered if they are deemed critical. We help you make the assessment.
When does NIS2 take effect?
The NIS2 directive was to be transposed into national law by 17 October 2024. In Sweden this is being implemented through a new cybersecurity act that has been delayed. Follow the Government Offices and MSB for the exact date. The requirements cover far more organizations than before, so preparation should start now.
What does NIS2 require of us?
NIS2 sets requirements for risk management, incident reporting, continuity and management-level accountability for organizations classed as important or essential. We help you determine whether you are in scope and produce an action plan that covers the requirements.
What is the difference between NIS2 and GDPR?
GDPR protects personal data. NIS2 is about operational security and resilience in essential and important services. They overlap in the security work but have different supervision and different requirements. We help you handle both in one action plan.
What does the Cyber Resilience Act (CRA) mean?
The CRA sets security requirements for products with digital elements sold in the EU: both for the product itself and for how vulnerabilities are handled across the lifecycle. If you build or sell such a product, you should start adapting now.
How do you prepare for the Cyber Resilience Act?
The CRA entered into force in 2024. Vulnerability reporting obligations start after about 21 months and the full product requirements after 36 months. Start by inventorying which of your products are in scope, build in security from the start, set up a vulnerability-handling process and prepare technical documentation.
Can you help with NIS2 and GDPR at the same time?
Yes. Much of the security and governance work is shared, so we produce one action plan that covers both regulations instead of running them as two separate tracks.
Working with Comitt
Can you step in as interim IT manager?
Yes. We can take the role of acting IT manager or provide IT expertise on the leadership team, full or part time, until you have a permanent solution in place.
When do you need an interim IT manager?
Common situations are an IT manager who is leaving, a recruitment that needs bridging, a parental leave, an acquisition, or a larger transformation or security project that needs to be led. An interim IT manager keeps momentum and decision-making going through the transition.
What does an interim IT manager cost?
It depends on scope and time: part time or full time, the length of the engagement and how much operational responsibility the role carries. We give a fixed quote after an initial call.
Do we have to use Nisenta to hire you?
No. Nisenta is our own platform for ongoing compliance, but advisory and development engagements are entirely separate. Many combine them, but it is not a requirement.
Do you do AI-driven development?
Yes. We build custom software and internal tools and use AI to shorten the path from idea to production, with the same requirements on architecture, security and review as always.
Further reading (in Swedish)
Contact
Tell us what you need.
An interim IT manager or CIO, NIS2 advisory, a development project or questions about Nisenta. Write a few lines and we'll get back to you shortly.
Prefer email directly?
contact@comitt.se
Håkan Puusepp
Founder, Comitt